Online Become a Hacker
Master offensive penetration testing, Kali Linux cyber weapons, and defensive network security with 100% Practical Training, Real Target Simulations & Live Virtual Labs. Gain hands-on mastery over all 9 core hacking domains under senior certified mentorship at Nemcon Systems.
MUHAMMAD ARIF
 Certified Ethical Hacking Instructor
Online Become a Hacker
Master Hacking in Just 3 Months • Complete Training Program
Why Master Ethical Hacking at Nemcon Systems?
Learn how cybercriminals think so you can defeat them. Develop deep technical muscle memory through real offensive attack simulations and enterprise vulnerability remediation.
Zero Slide Theory
Forget endless PowerPoint lectures. From day one, you boot up Kali Linux, scan targets, exploit unpatched services, and build custom exploit payloads on real command-line terminals.
100% Practical Virtual SandboxOffensive & Defensive Balance
Learn both sides of cyber combat: launch attacks like a Red Teamer (Metasploit, Burp Suite), and harden systems like a Blue Teamer with firewalls, IDS sensors, and log analysis.
Red Team + Blue Team SkillsBug Bounty & Freelance Scope
Learn how to ethically hunt vulnerabilities on platforms like HackerOne and Bugcrowd. Earn high-paying dollar rewards from the comfort of your home in Lahore.
Earn Bounties GloballyComplete Hacking Course Covers 9 Powerful Domains
Comprehensive 3-month curriculum reverse-engineered from real cyber warfare scenarios and aligned directly with global CEH standards.
D01 1. Introduction to Hacking
Domain 1 • Core Principles, Attack Lifecycle, Legalities & Kali Linux Setup
1. Introduction to Hacking
Domain 1 • Core Principles, Attack Lifecycle, Legalities & Kali Linux Setup
Understand ethical hacking concepts, legal compliance (PECA 2016), attack life cycles, and configure an enterprise-grade isolated virtual laboratory.
- Ethical hacking fundamentals, code of ethics, and PECA 2016 cyber laws
- Hacker categories: White Hat, Gray Hat, Black Hat & Threat Actors
- Anatomy of an attack: Reconnaissance, Scanning, Gaining Access, Maintaining Access & Clearing Tracks
- Setting up Kali Linux and isolated virtual targets (VMware / VirtualBox)
- Essential Linux command-line tools, permissions, bash scripting & networking essentials
D02 2. Reconnaissance & Footprinting
Domain 2 • OSINT, Threat Vectors, Google Dorking & Target Attack Surface
2. Reconnaissance & Footprinting
Domain 2 • OSINT, Threat Vectors, Google Dorking & Target Attack Surface
Master active and passive intelligence gathering to map an organization's digital footprint before launching targeted attacks.
- Passive Reconnaissance: Google Hacking Database (GHDB) & advanced dorking
- Open Source Intelligence (OSINT) with Maltego, theHarvester & SpiderFoot
- WHOIS record investigation, DNS interrogation & zone transfer testing
- Shodan, Censys & SecurityTrails for discovering exposed servers and ports
- Compiling exhaustive pre-attack target dossiers
D03 3. Network Scanning & Enumeration
Domain 3 • Nmap Port Scanning, Banner Grabbing & Deep Packet Inspection
3. Network Scanning & Enumeration
Domain 3 • Nmap Port Scanning, Banner Grabbing & Deep Packet Inspection
Locate active live hosts, probe open ports, uncover running service versions, and capture raw network packets for deep protocol analysis.
- TCP Three-Way Handshake analysis & TCP flag states (SYN, ACK, FIN, RST)
- Nmap scan techniques (SYN Stealth, UDP, Null, FIN, Xmas scans)
- Nmap Scripting Engine (NSE) for automated vulnerability detection
- Service banner grabbing, OS fingerprinting, and SMB/SNMP enumeration
- Packet sniffing and protocol dissection with Wireshark
D04 4. Vulnerability Assessment & Management
Domain 4 • Automated Flaw Scanning, CVSS Scoring & Patch Remediation
4. Vulnerability Assessment & Management
Domain 4 • Automated Flaw Scanning, CVSS Scoring & Patch Remediation
Identify unpatched software vulnerabilities, rank flaw severity using international CVSS v3.1 frameworks, and build corporate remediation strategies.
- Vulnerability scanning lifecycle and enterprise audit policies
- Enterprise scanning with Tenable Nessus and OpenVAS
- Common Vulnerabilities and Exposures (CVE) analysis & Exploit-DB correlation
- CVSS v3.1 scoring: Base, Temporal, and Environmental metrics
- Compiling executive risk scorecards and remediation roadmaps
D05 5. System Hacking & Exploitation
Domain 5 • Metasploit Framework, Meterpreter, Password Cracking & PrivEsc
5. System Hacking & Exploitation
Domain 5 • Metasploit Framework, Meterpreter, Password Cracking & PrivEsc
Gain root and administrator access on vulnerable Windows Server and Linux machines, extract password hashes, and maintain persistent backdoors.
- Metasploit Framework architecture (exploits, payloads, encoders, post modules)
- Meterpreter payload execution, process migration & keystroke logging
- Exploiting remote vulnerabilities (SMB EternalBlue MS17-010, RDP BlueKeep)
- Local Privilege Escalation (PrivEsc) on Linux (SUID) and Windows (Token abuse)
- High-speed password cracking with Hydra, Hashcat, and John the Ripper
D06 6. Web Application & API Security
Domain 6 • Burp Suite Proxy, OWASP Top 10, SQLi, XSS, CSRF & Bug Bounty
6. Web Application & API Security
Domain 6 • Burp Suite Proxy, OWASP Top 10, SQLi, XSS, CSRF & Bug Bounty
Intercept web traffic, bypass security controls, and discover critical vulnerabilities in modern web applications and REST APIs to earn global bug bounties.
- Burp Suite Professional setup, Intercept Proxy, Repeater & Intruder
- OWASP Top 10 vulnerabilities (SQL Injection, XSS, CSRF, IDOR, SSRF)
- SQL Injection exploitation (error, union, blind) with SQLmap automation
- Cross-Site Scripting (Reflected, Stored, DOM) & session hijacking
- REST API security testing, Broken Object Level Authorization (BOLA/IDOR)
- Bug bounty hunting methodology on HackerOne & Bugcrowd
D07 7. Social Engineering & Human Hacking
Domain 7 • Phishing Simulations, Credential Harvesting & Social-Engineer Toolkit
7. Social Engineering & Human Hacking
Domain 7 • Phishing Simulations, Credential Harvesting & Social-Engineer Toolkit
Exploit the human element through psychological manipulation, craft targeted spear-phishing attacks, and learn defensive awareness training.
- Psychological attack principles: Authority, Urgency, Scarcity & Familiarity
- Automated spear-phishing campaigns with Social-Engineer Toolkit (SET)
- Credential harvester attacks and cloning corporate login portals
- Pretexting, malicious USB drop attacks, and reverse social engineering
- Defending against human hacking with security culture training
D08 8. Wireless Network Security
Domain 8 • 4-Way Handshake Cracking, Deauth Attacks, Rogue APs & MitM
8. Wireless Network Security
Domain 8 • 4-Way Handshake Cracking, Deauth Attacks, Rogue APs & MitM
Analyze radio signal frames, intercept wireless transmissions, capture encryption handshakes, and execute Man-in-the-Middle network manipulations.
- 802.11 Wi-Fi frames: Management, Control & Data frame dissection
- Putting wireless adapters into Monitor Mode with airmon-ng
- Deauthentication attacks and capturing WPA/WPA2 4-Way Handshakes
- High-speed GPU handshake cracking with custom wordlists
- Rogue Access Points, Evil Twin attacks & Man-in-the-Middle (MitM) with Bettercap
D09 9. Cloud, IoT & OT Security
Domain 9 • AWS/Azure Cloud Auditing, S3 Bucket Leaks, IoT & ICS/SCADA
9. Cloud, IoT & OT Security
Domain 9 • AWS/Azure Cloud Auditing, S3 Bucket Leaks, IoT & ICS/SCADA
Assess cloud infrastructure flaws, examine Internet of Things (IoT) hardware firmware, and understand critical Operational Technology (OT) defense.
- Cloud Shared Responsibility Model (AWS, Azure, GCP)
- Discovering publicly exposed AWS S3 buckets & cloud blob storage
- Cloud IAM privilege escalation and auditing with ScoutSuite
- Internet of Things (IoT) attack vectors, weak credentials & firmware extraction
- Operational Technology (OT) and SCADA/ICS industrial control security overview
Need the Complete 9-Domain Syllabus PDF?
Download the detailed week-by-week lab schedule, virtual range topologies, and tool installation handbook.
25+ Industry Cyber Weapons & Lab Environment
Practice on real tools used by ethical hackers, government penetration testers, and Fortune 500 security analysts.
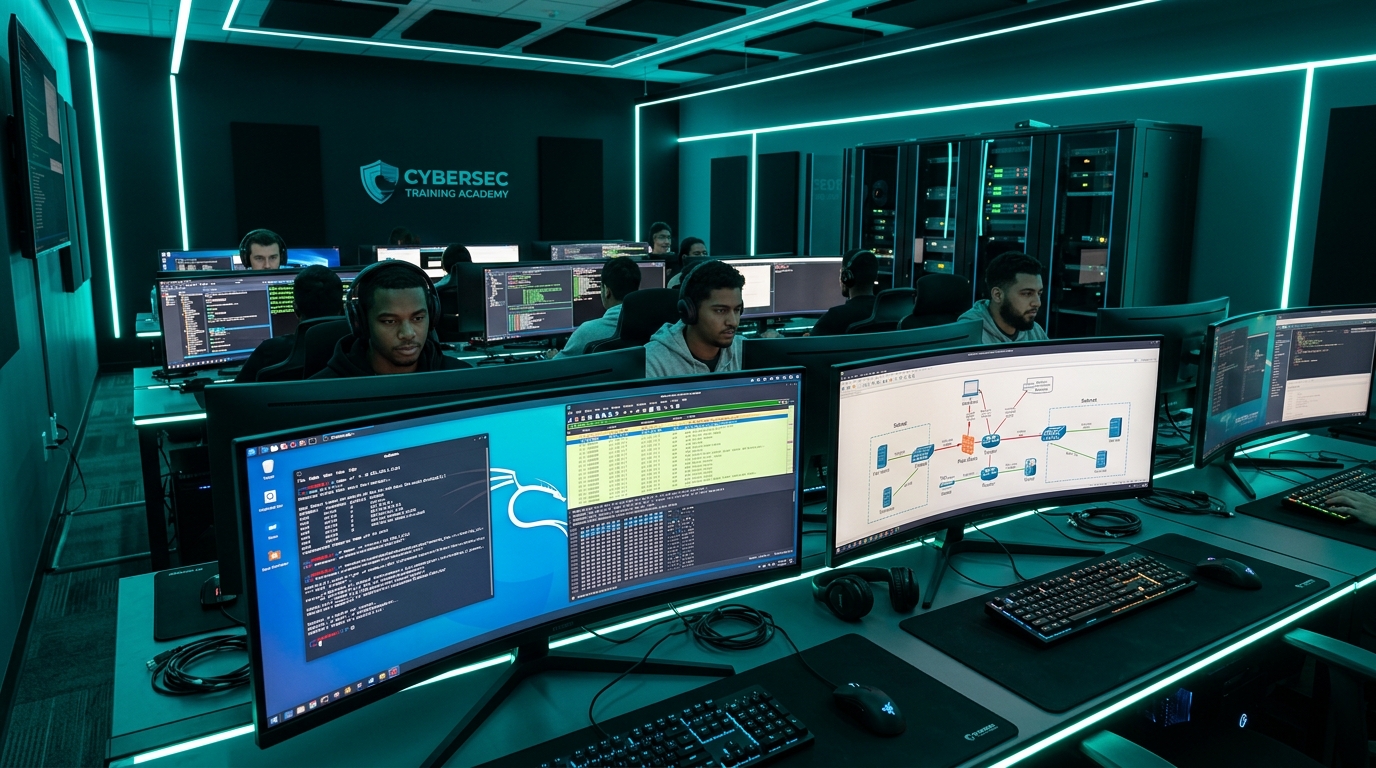
Red Team Attack Range: Kali Linux & Metasploit Exploitation
Execute exploits against Metasploitable 2 & 3, vulnerable Windows Active Directory domains, and OWASP web targets inside an isolated virtual sandbox.
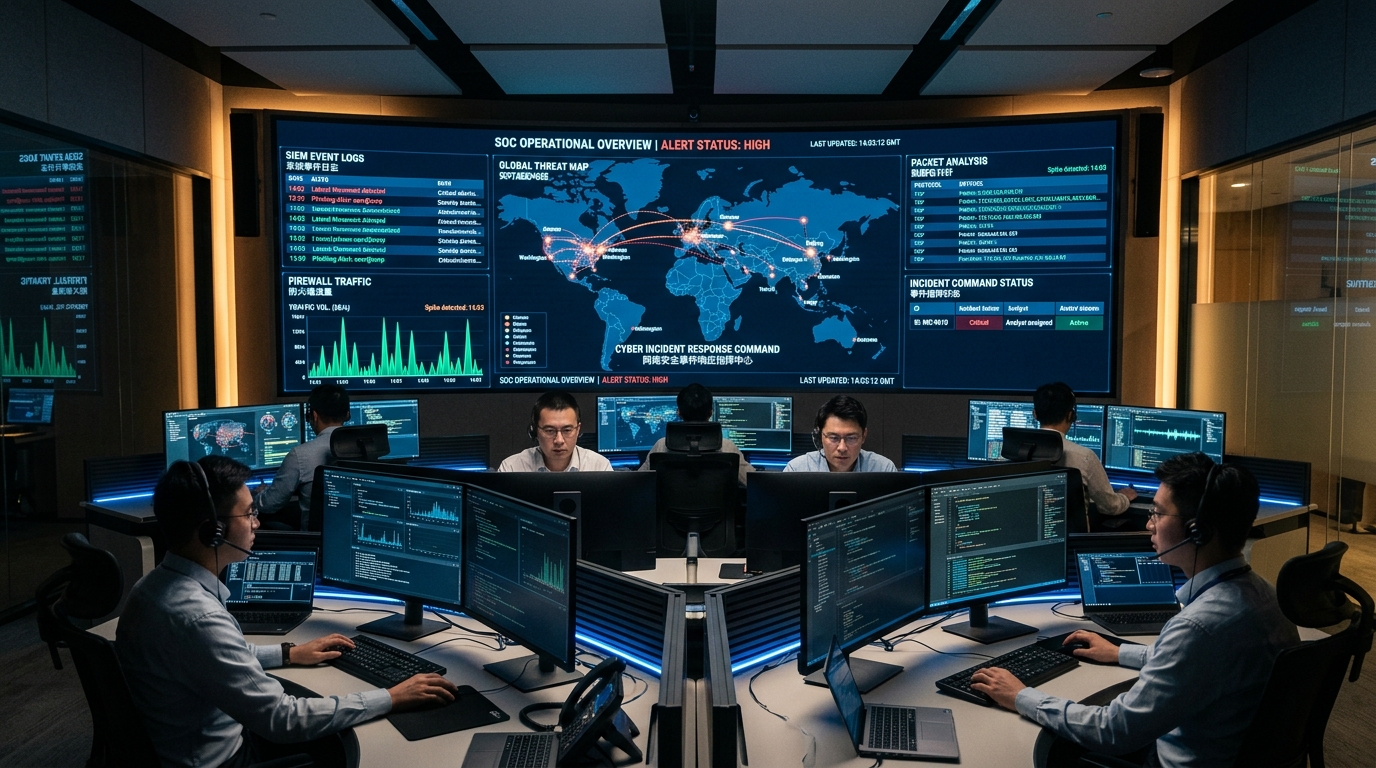
Defensive Countermeasures: Wazuh SIEM & Snort Telemetry
Understand what defenders see. Observe real attack telemetry in Wazuh SIEM dashboards, dissect packet captures in Wireshark, and write mitigation firewall rules in pfSense.
Tools & Frameworks Mastered During Training:
Who Should Enroll & Prerequisites
Designed for aspiring cybersecurity professionals, university graduates, and IT administrators looking to transition into ethical hacking.
- Computer Science & IT Students
Build real practical experience outside academic theory and graduate with job-ready penetration testing portfolios.
- Network & System Administrators
Upgrade your skillset from regular administration to high-paying network security and cyber defense engineering.
- Aspiring Bug Bounty Hunters
Learn structured web application security auditing methodology to earn US dollar bounties on HackerOne and Bugcrowd.
- IT Support & Career Switchers
Transition into the zero-unemployment domain of information security with step-by-step mentor guidance.
We teach networking fundamentals, basic Linux commands, and security concepts from the ground up.
Recommended Laptop Specs for Labs:
- Processor: Intel Core i5 (8th Gen+) or AMD Ryzen 5
- RAM: 16 GB recommended (minimum 8 GB)
- Storage: 100 GB free SSD storage for virtual machines
- Operating System: Windows 10/11, macOS, or Linux host
Onsite students in Lahore also get access to dedicated high-performance lab workstations at our campus.
Common Questions About Ethical Hacking in Lahore
Find answers to the most common queries regarding course fees, batch schedules, certifications, and career scope.
What is the fee for the Hacking Course at Nemcon Systems?
The fee is Rs. 25,000 per month, totaling Rs. 75,000 for the complete 3-month intensive practical hacking course covering all 9 domains and CEH-aligned labs. The same discounted monthly fee applies for all 3 months of the training program.
Do I need a coding or computer science background to join this course?
No prior programming or computer science degree is required. Our instructors start from basic computer networking (IP addresses, subnets, ports, OSI layers) and fundamental Linux terminal navigation before advancing to penetration testing tools. Anyone with curiosity and basic computer literacy can succeed.
Is an official certification provided upon course completion?
Yes. Upon completing all laboratory assignments and the capstone penetration testing project, students receive an official, industry-recognized Certificate in Ethical Hacking & Penetration Testing from Nemcon Systems (serving Pakistan since 2006). The syllabus also thoroughly prepares you for the international Certified Ethical Hacker (CEH v13) certification.
Are the lab sessions 100% hands-on and practical?
Yes! 100% of our training is lab-driven. Every student configures their own isolated virtual attack range using Kali Linux, Metasploitable targets, Windows Active Directory servers, and deliberately vulnerable web applications without touching theoretical slides.
Is ethical hacking legal in Pakistan, and what laws are covered?
Ethical hacking is 100% legal when performed with written authorization and clear rules of engagement. We strictly educate students on ethical boundaries and compliance with Pakistan's Prevention of Electronic Crimes Act (PECA 2016) and global cyber laws. All attack simulations occur strictly within our isolated virtual labs.
What job opportunities and freelance bug bounty prospects exist after graduation?
Graduates qualify for high-demand IT security roles such as Junior Penetration Tester, SOC Analyst (Tier 1), Information Security Officer, and Vulnerability Analyst in local banks, software houses, and telecom operators. Furthermore, we mentor students on how to legally report vulnerabilities on HackerOne and Bugcrowd to earn US dollar bounties from home.
Ready to Become a Certified Ethical Hacker?
Register at Nemcon Systems Lahore today. Master offensive Kali Linux tools, web application security, and network penetration testing with 100% hands-on virtual lab access.